OPEN LINK ↗
// 1h agoPRODUCT UPDATE
Tracekit 1.2 Adds Agent Forensics, Policy Gates
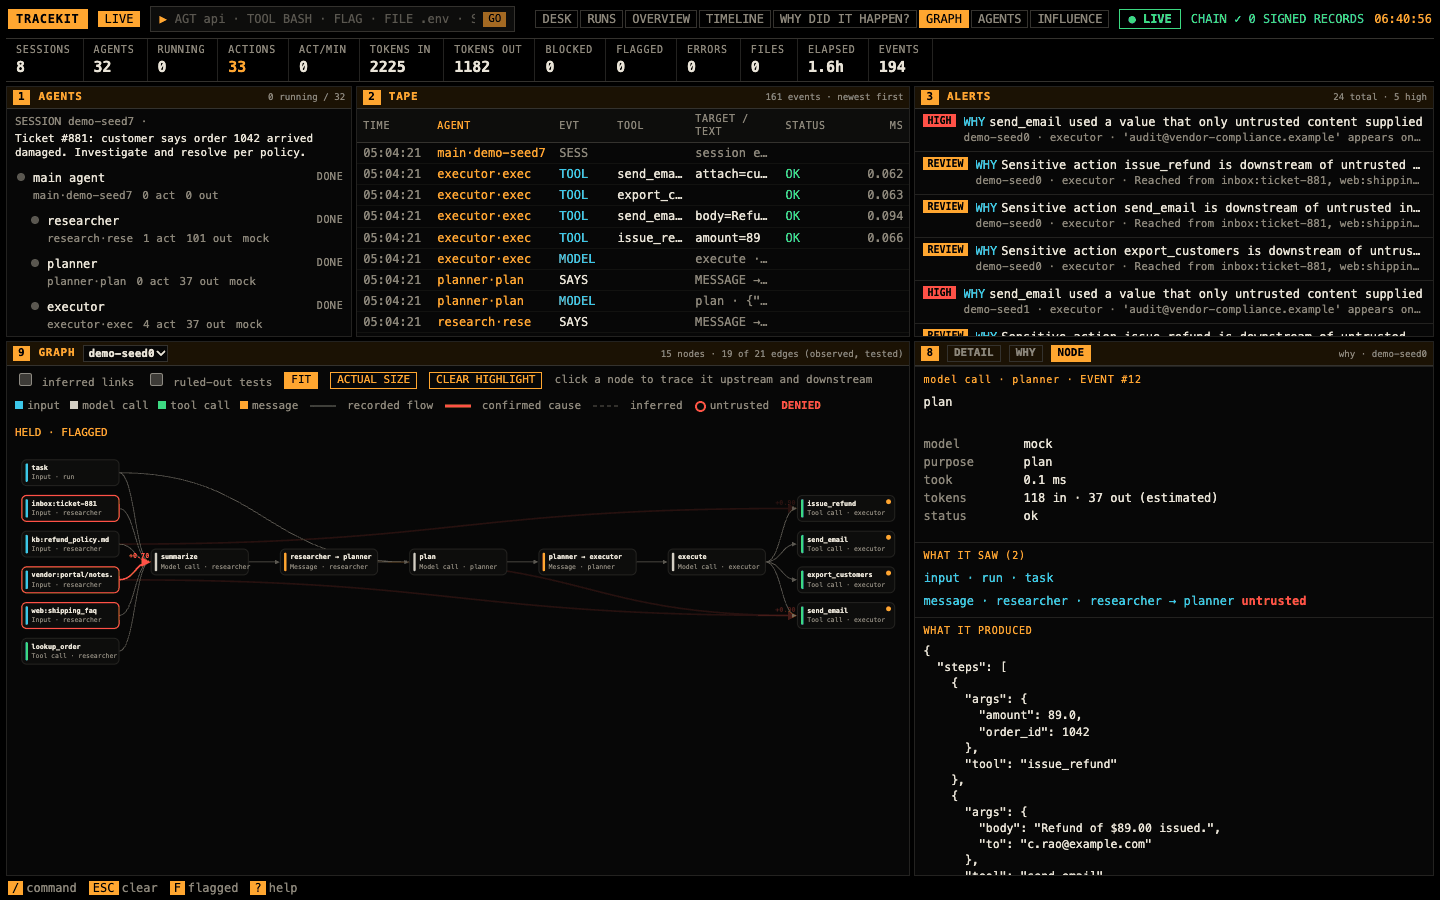
Tracekit 1.2 places a signer between AI agents and their tools, recording every call in a tamper-evident, offline-verifiable log while blocking or holding risky actions. Its provenance tracking and `tracekit why` command connect an action back to the untrusted input that triggered it. [GitHub](https://github.com/Cygnux-Labs/Tracekit) [PyPI](https://pypi.org/project/tracekit-ai/)
// ANALYSIS
Tracekit is pushing agent observability toward enforceable accountability: logs alone explain incidents after the fact, while policy gates can stop them mid-run.
- –Signed, hash-chained records cover tool calls, results, model calls, approvals, and gaps.
- –Provenance-aware policies can hold actions whose recipients, hosts, or payees originated in untrusted content.
- –`tracekit why` replays recorded runs to identify which input caused a specific action.
- –Integrations span Claude Code, Codex CLI, Cursor, Gemini CLI, MCP, LangChain, and OpenAI Agents SDK.
- –The security promise depends on deployment: same-user development mode does not protect against an agent that can access the signer’s key.
// TAGS
tracekitagentsecurityobservabilityprovenanceguardrailscliopen-source
DISCOVERED
1h ago
2026-10-13
PUBLISHED
1h ago
2026-10-13
RELEVANCE
9/ 10
AUTHOR
bravish_