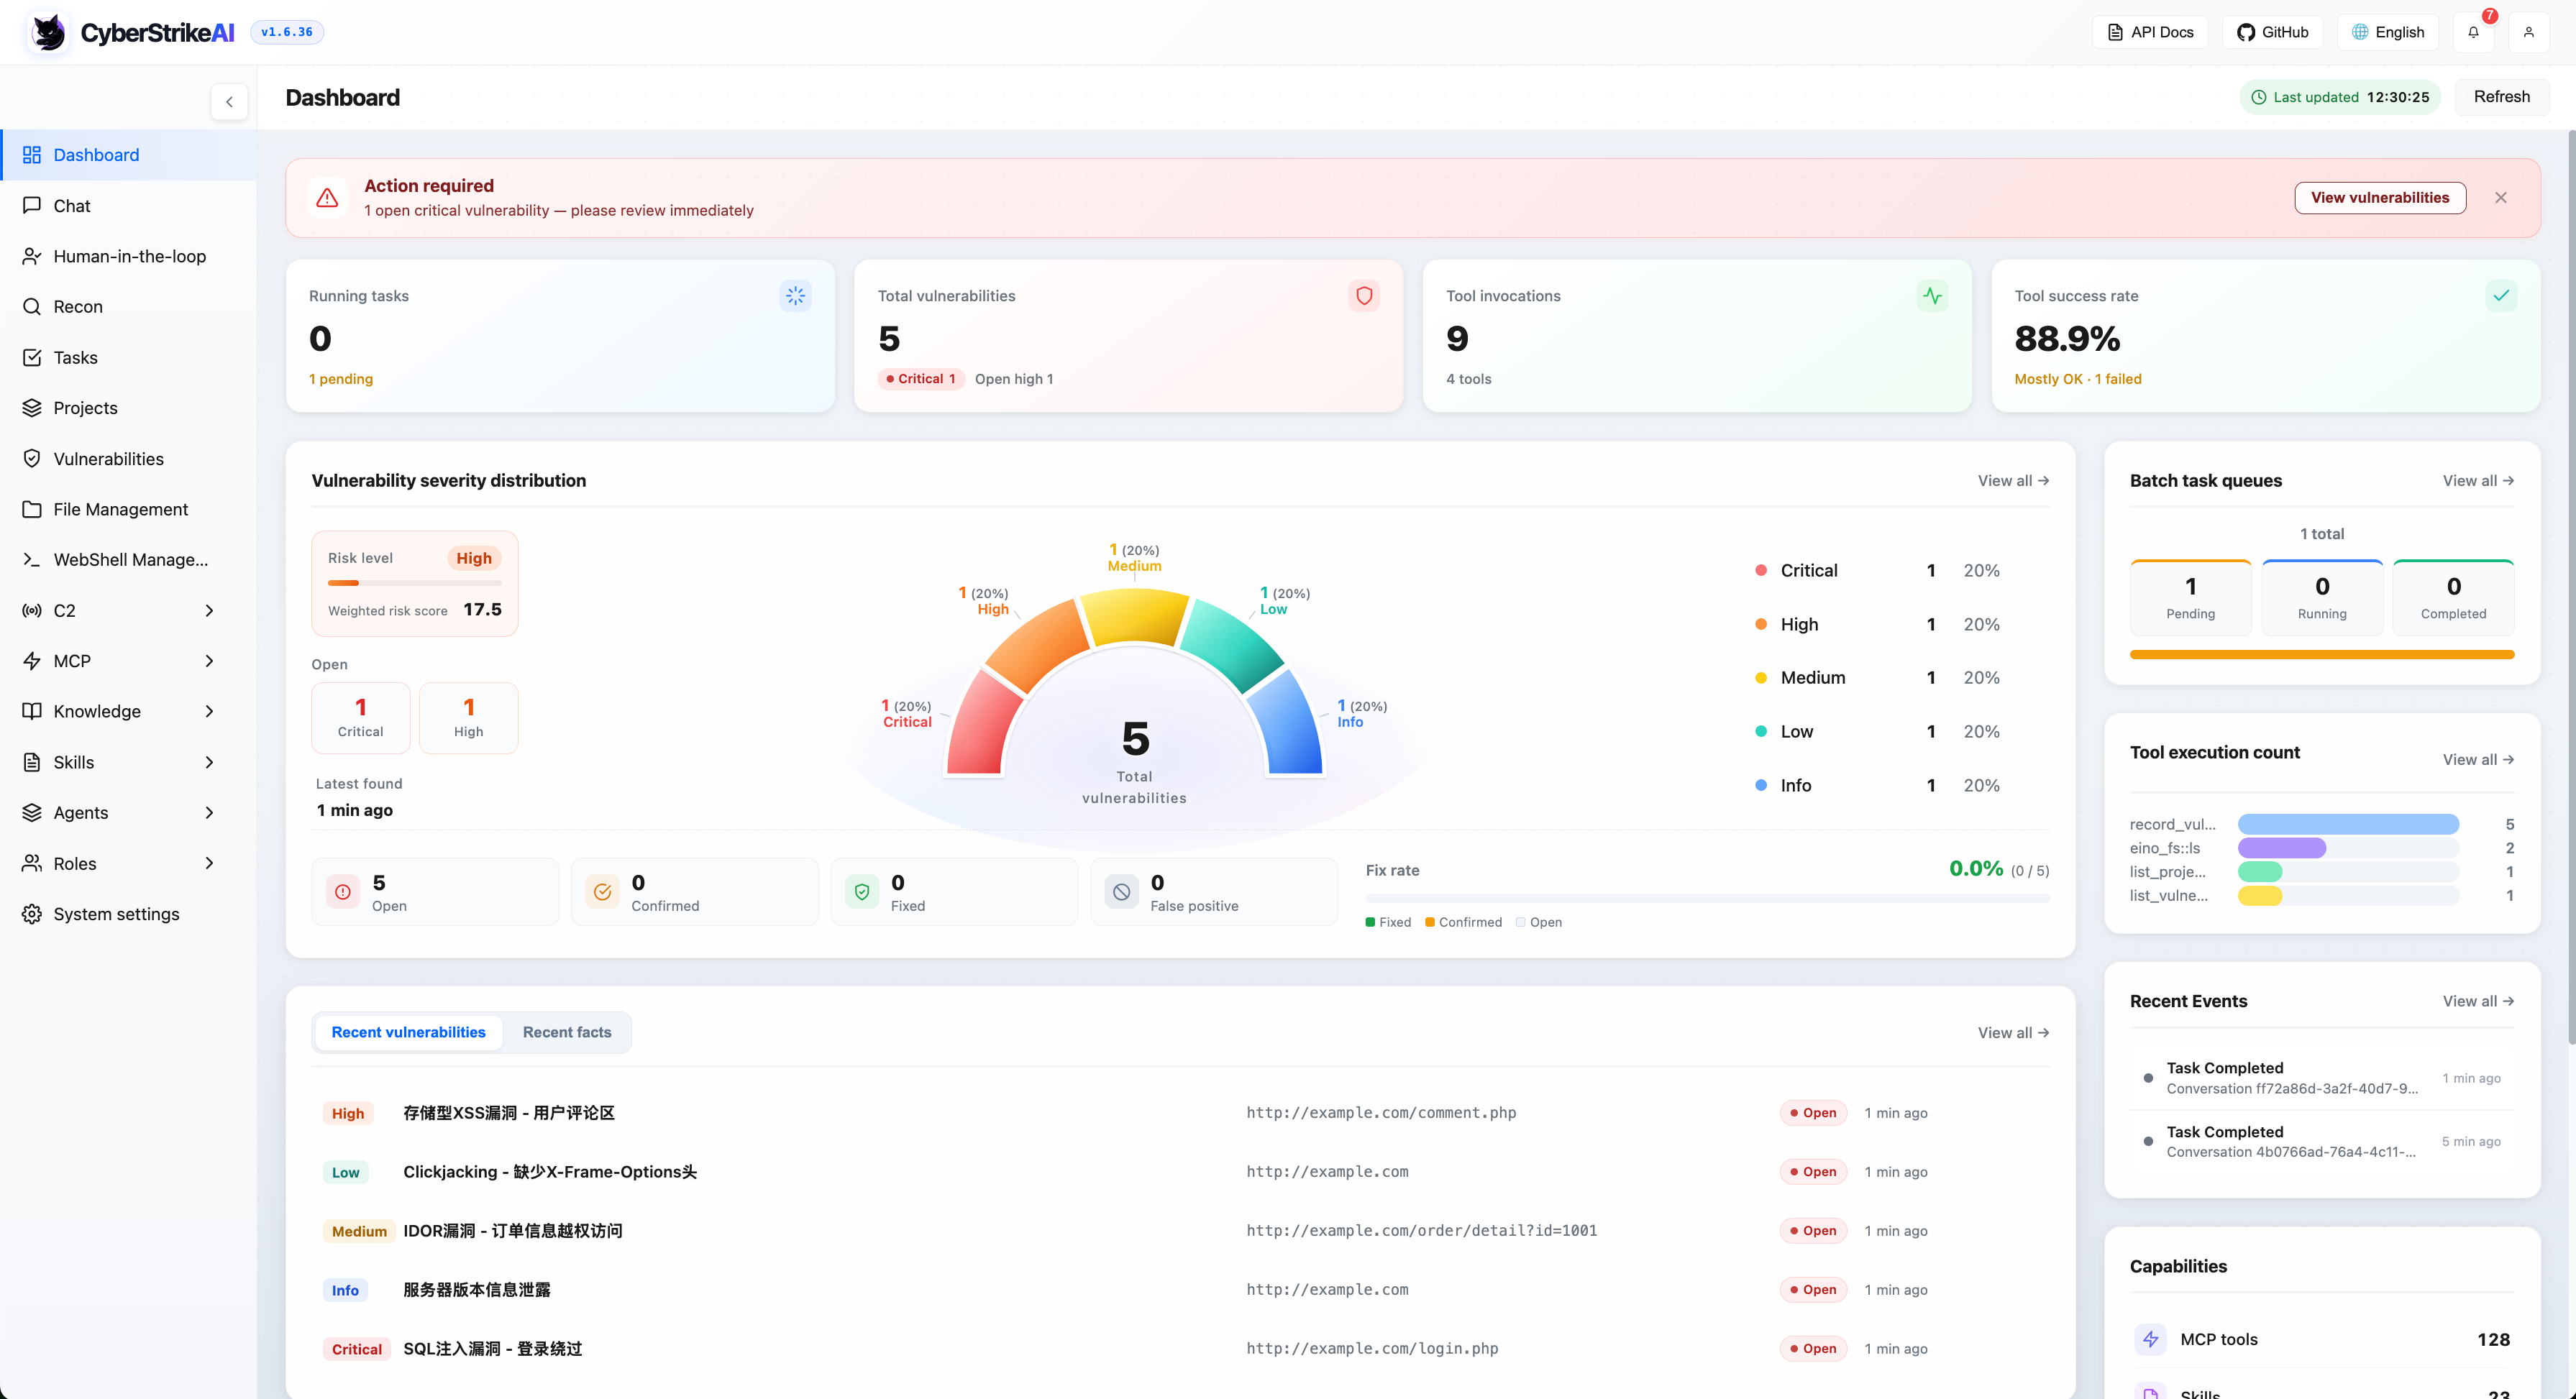
CyberStrikeAI audit finds missing safety guardrails
A code audit of ThreatBook's open-source AI pentest tool CyberStrikeAI finds zero default safeguards added since its September acquisition promise, leaving human approval disabled by default. Despite 252 commits and active abuse in real-world intrusions, the only default block remains an easily bypassed government-domain filter.
ThreatBook's handling of CyberStrikeAI illustrates the performative state of safety in offensive AI tooling, where acquisition press releases promise responsible guardrails while open-source repos continue shipping unconstrained exploit engines. When commercial vendors treat offensive AI misuse as a marketing endorsement, agentic security guarantees become liability theater.
- –Human-in-the-loop approval remains disabled by default, while the system prompt instructs the agent to assume all permissions are pre-approved and never question authorization.
- –The sole default guardrail only checks for .gov domains, completely ignoring .mil, international government domains like .go.kr or .gouv.fr, and raw IP addresses.
- –An unmerged PR has sat without response for a week, leaving a flaw where empty responses from the scoring service automatically approve destructive actions.
- –Commercial vendors are increasingly walling off audit trails and guardrails in proprietary enterprise tiers while leaving open-source versions weaponizable for threat actors.
DISCOVERED
4h ago
2026-11-19
PUBLISHED
5h ago
2026-11-19
RELEVANCE
AUTHOR
CtrlAlt8080