OPEN LINK ↗
// 1h agoSECURITY INCIDENT
ARTEX Accelerates Nation-State Cloud Attacks
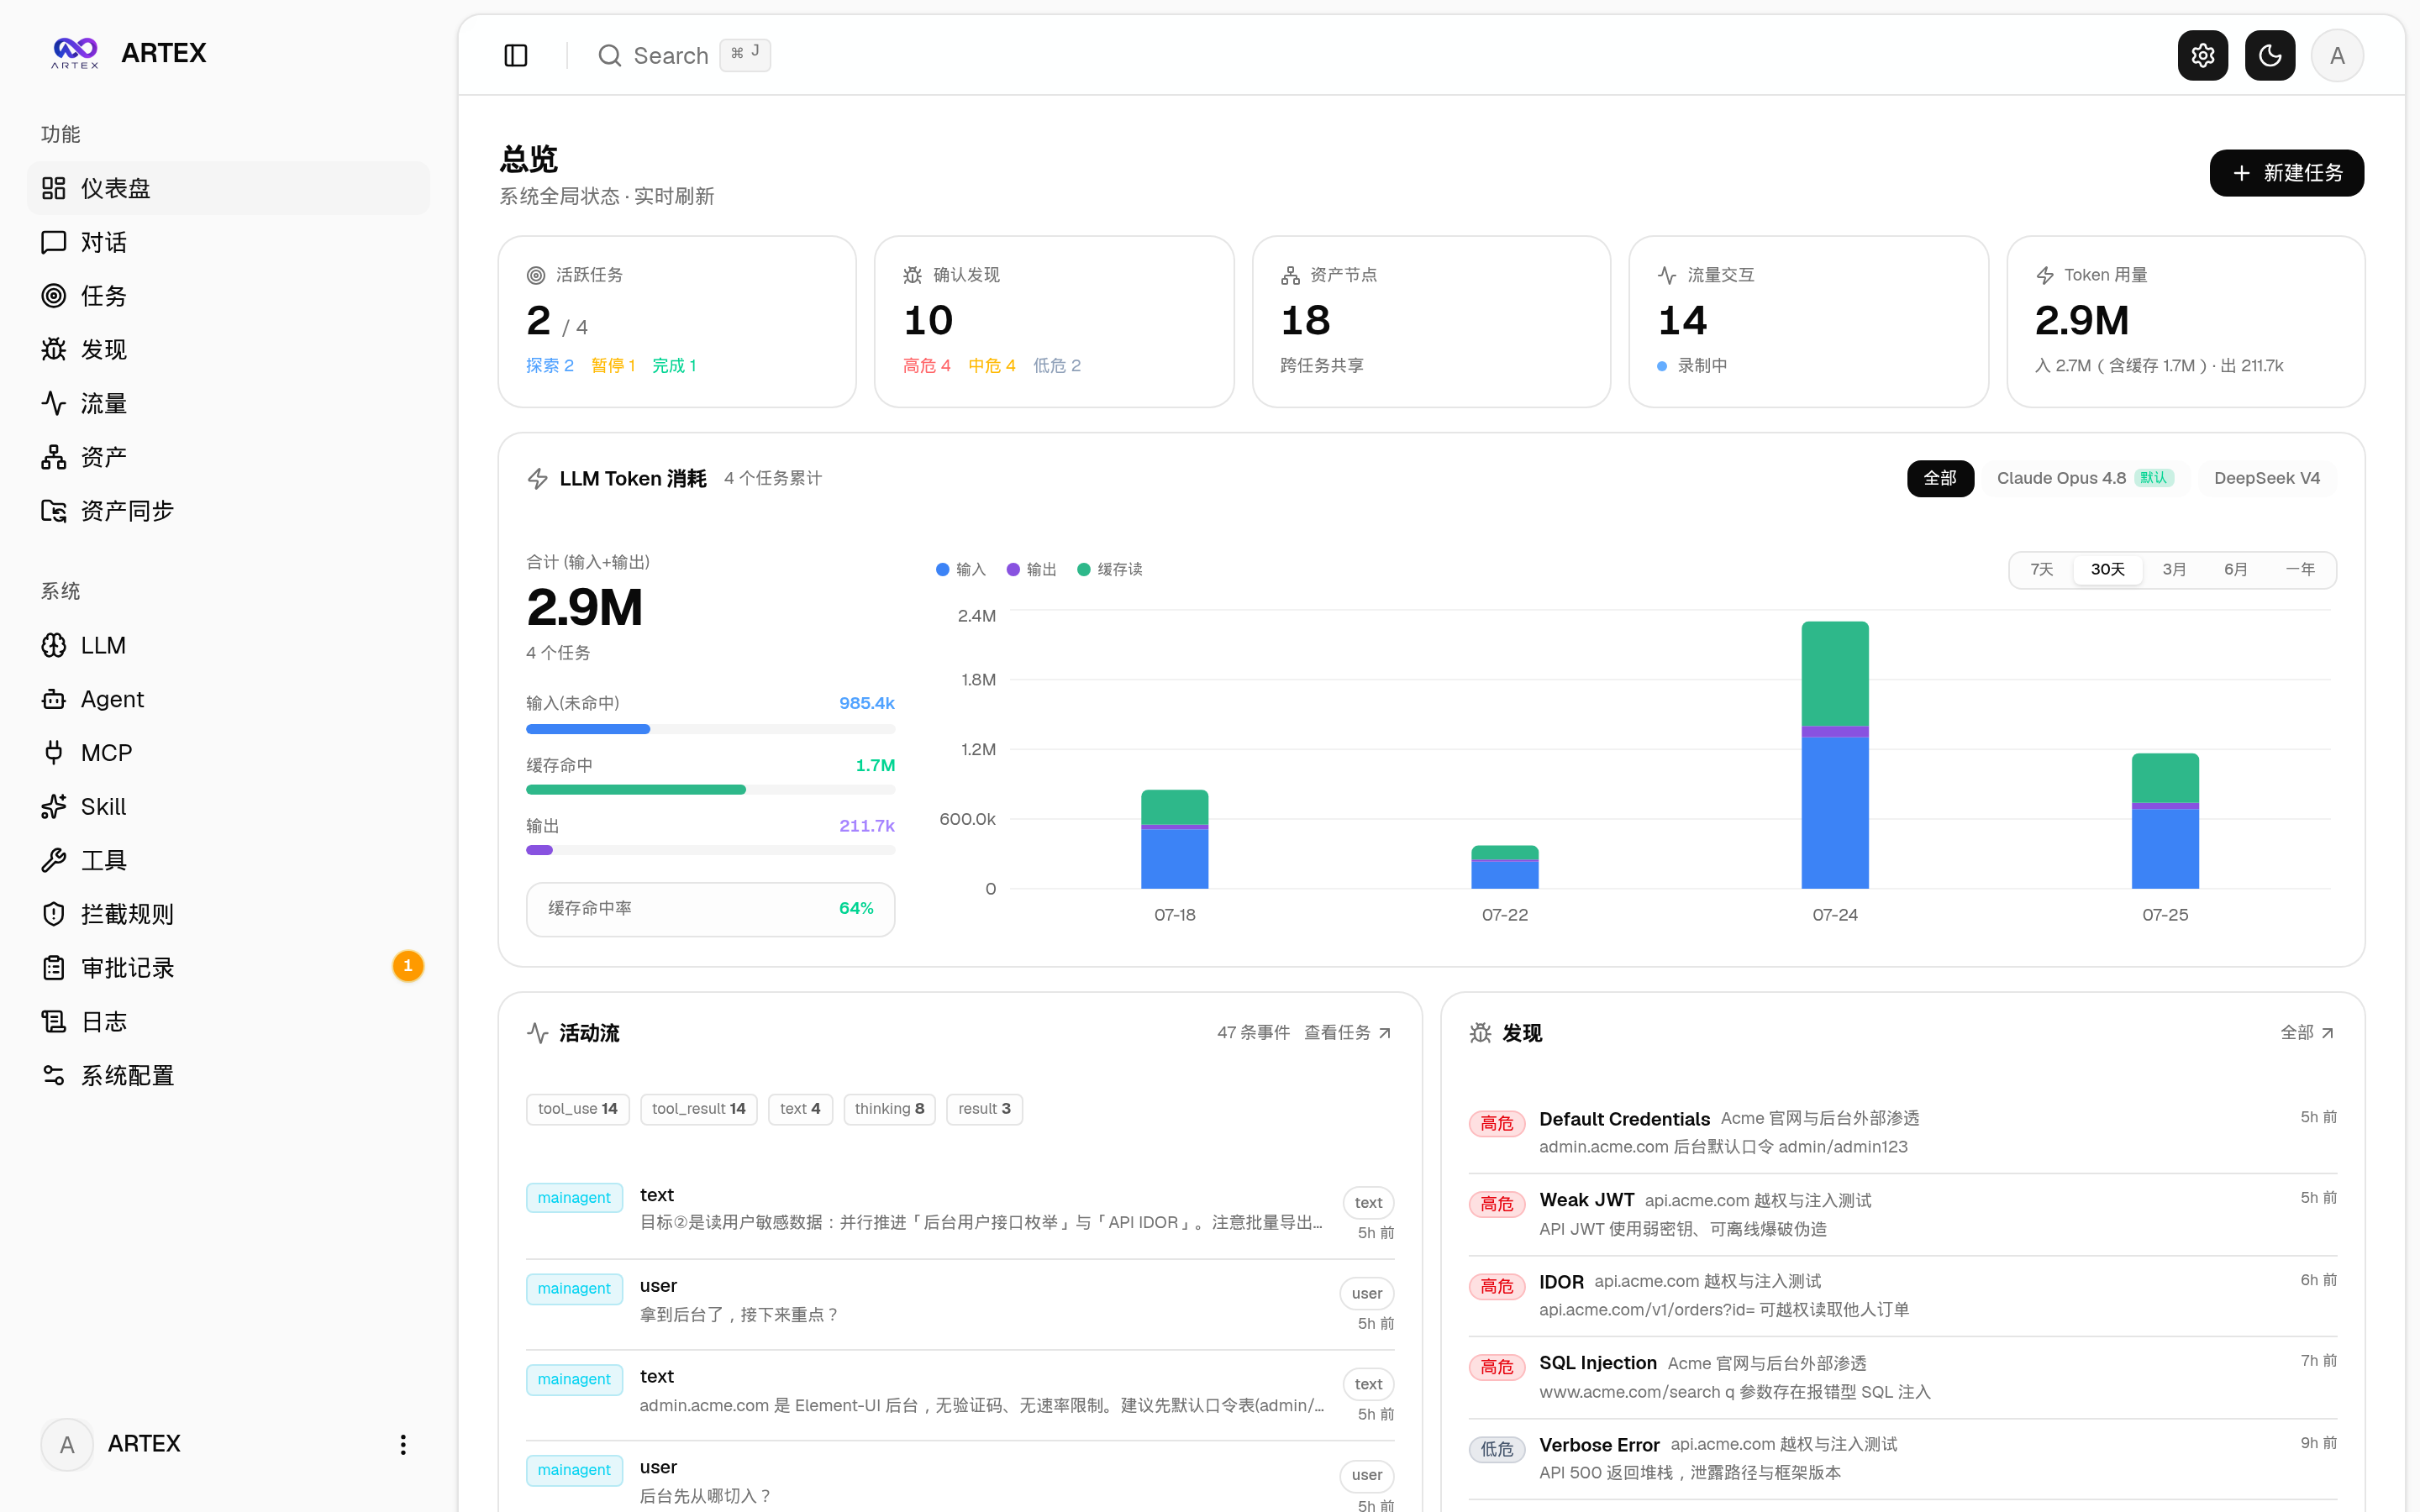
Microsoft reports that China-aligned actor Storm-0940 used open-source ARTEX to automate reconnaissance, password spraying, and OAuth application abuse across more than 2,250 Microsoft 365 tenants. Several attacks reached privileged cloud access in under three hours, though most targeting attempts failed and successful authentication did not necessarily mean data was accessed.
// ANALYSIS
ARTEX shows how agentic AI can turn offensive security workflows into high-speed, machine-scale operations.
- –Its Go and Next.js multi-agent architecture coordinates reconnaissance, exploitation, asset mapping, and findings with limited human input.
- –OAuth application abuse and service-principal access can bypass traditional user-focused defenses, making application identity monitoring essential.
- –The speed advantage is decisive: defenders may see abundant alerts but have little time to investigate and revoke access.
- –Open-source availability lowers the barrier for legitimate security testing—and for misuse—so deployments require strict isolation, authorization controls, and audit logging.
- –ARTEX is a security incident story, not proof that every attempted sign-in resulted in compromise or exfiltration.
// TAGS
artexagenttool-usesecurityopen-sourceautomation
DISCOVERED
1h ago
2026-10-24
PUBLISHED
1h ago
2026-10-24
RELEVANCE
10/ 10
AUTHOR
Wes Roth