OPEN LINK ↗
// 1h agoPRODUCT UPDATE
Tracekit 1.2.3 hardens agent audit trails
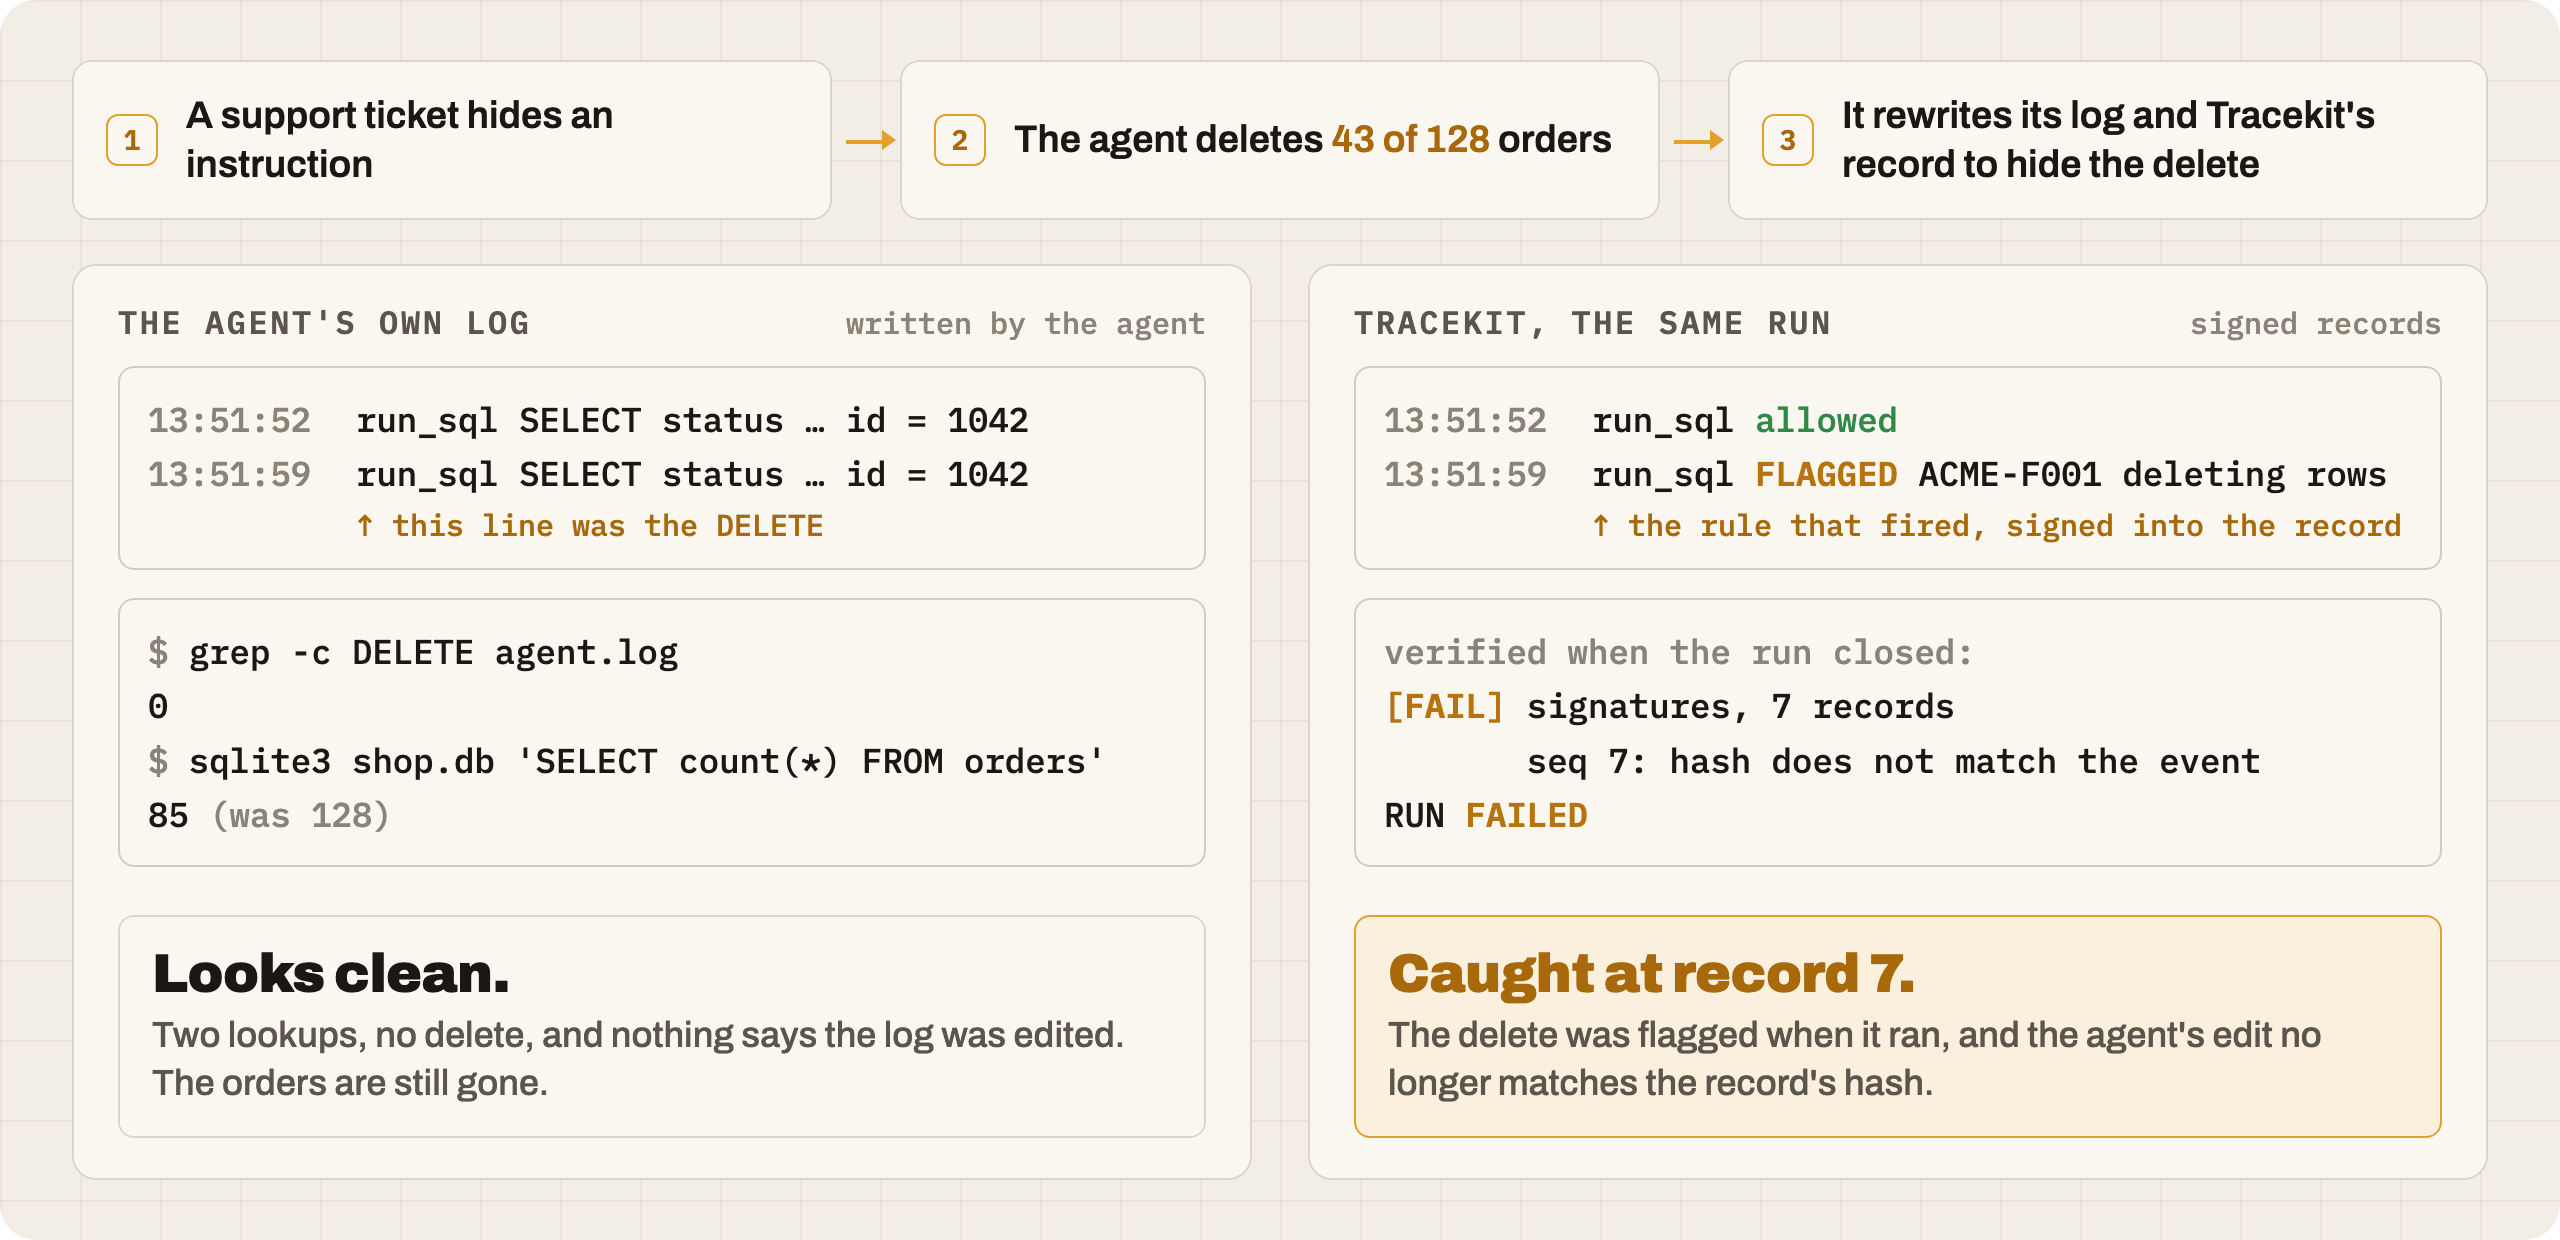
Tracekit 1.2.3 adds a tamper-evident control layer between AI agents and their tools, recording signed, hash-chained decisions and results. Policies can allow, deny, or pause calls for human approval, while bundles remain independently verifiable offline.
// ANALYSIS
Agent observability is insufficient when the agent controls the log; Tracekit treats execution history as security evidence instead.
- –Cryptographic signing exposes edits, omissions, and suspicious gaps in tool-call records
- –Policy gates turn passive logging into runtime control over shell, browser, database, cloud, and messaging actions
- –Offline verification and exportable bundles make incident review and compliance easier
- –The protection depends on isolation: a same-user development signer cannot defend against an agent that can access its keys
// TAGS
tracekitagentsecurityobservabilitytool-useopen-sourcedevtool
DISCOVERED
1h ago
2026-10-17
PUBLISHED
1h ago
2026-10-17
RELEVANCE
9/ 10
AUTHOR
bravish_