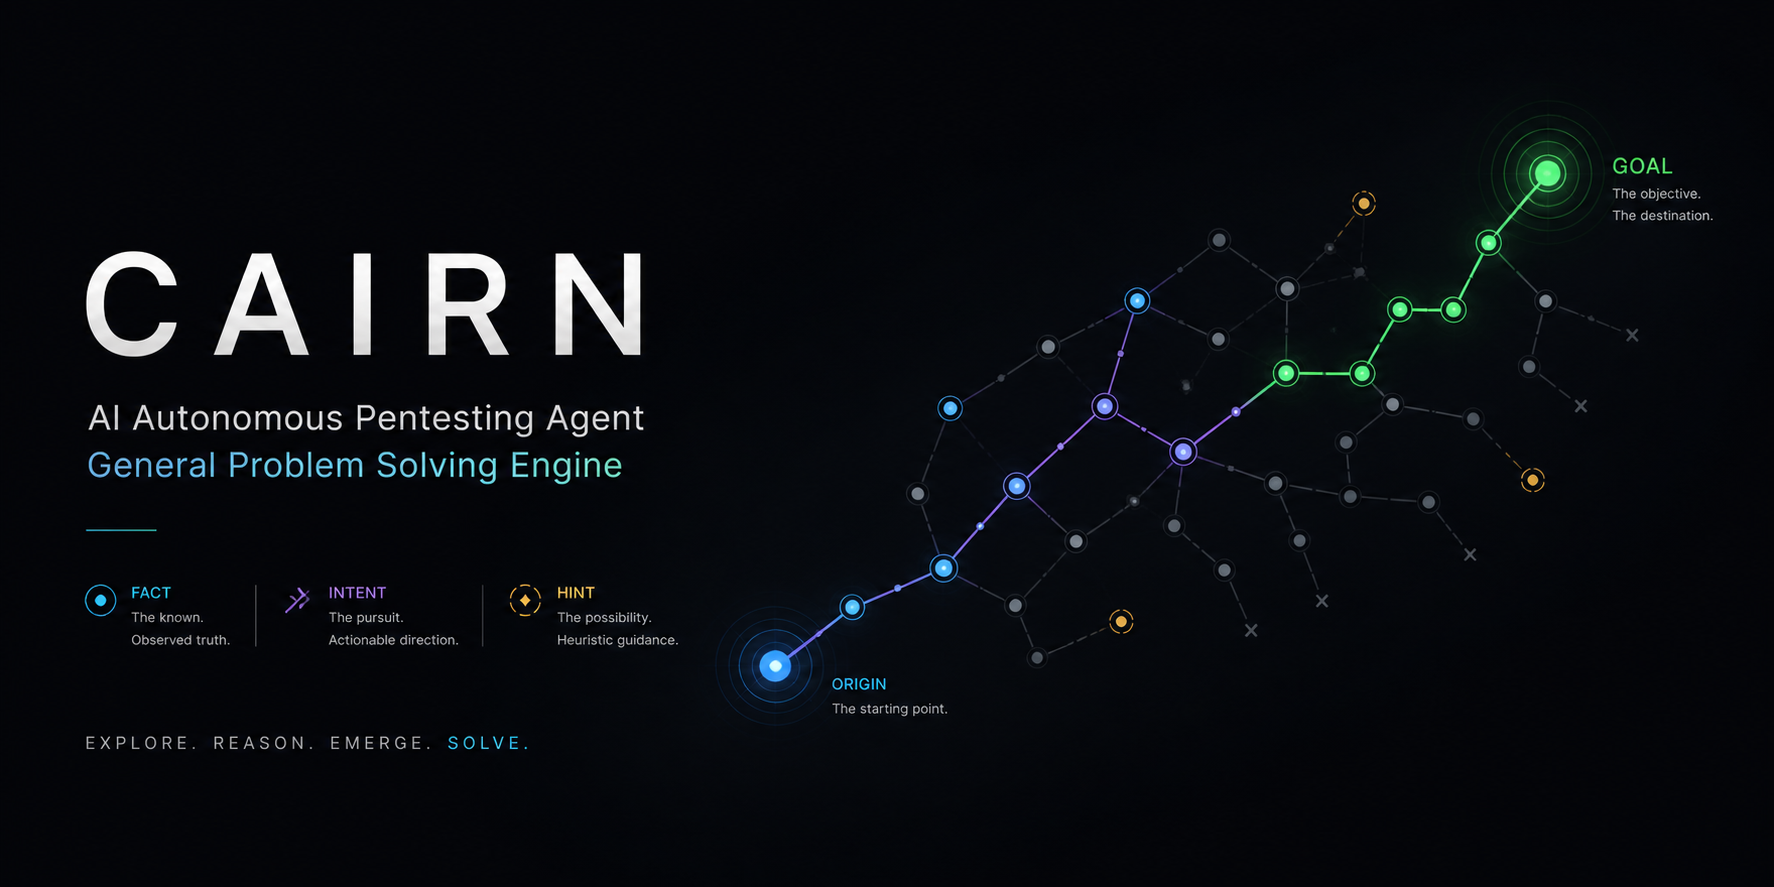
Cairn Agents Breach 100+ Company Sites
NorForge found exposed Cairn panels directing AI agents against roughly 1,200 sites, with Reuters reporting more than 100 company websites breached, including Deere and SharkNinja. Cairn’s autonomous, state-space problem-solving architecture let agents probe vulnerabilities and pursue persistent access with minimal human supervision. [NorForge](https://norforge.com/blog/inside_cairn) [Reuters report](https://www.investing.com/news/stock-market-news/exclusivehow-one-hacker-used-ai-agents-and-a-few-thousand-dollars-to-break-into-scores-of-sites-4956846)
The alarming shift is economic: open-ended agents turn neglected web inventory into a scalable intrusion queue, making basic asset ownership and patching discipline more important than ever.
- –The campaign reportedly averaged about 23 hours per successful intrusion, with estimated model costs near $50 each.
- –Standalone support pages and vendor-operated sites can be softer targets than flagship domains, yet still carry the brand’s trust.
- –Cairn’s shared blackboard lets agents retain facts, choose new actions, and pivot when an attack path stalls.
- –Developers should inventory every branded domain, subdomain, vendor deployment, and exposed control panel—and assign a named owner for each patch cycle.
- –Agent infrastructure needs authentication, network isolation, outbound restrictions, and long-running session monitoring by default.
DISCOVERED
1h ago
2026-10-22
PUBLISHED
1h ago
2026-10-22
RELEVANCE
AUTHOR
Lewis502