OPEN LINK ↗
// 46d agoINFRASTRUCTURE
Prismor Makes Agent Runtime Security Layered
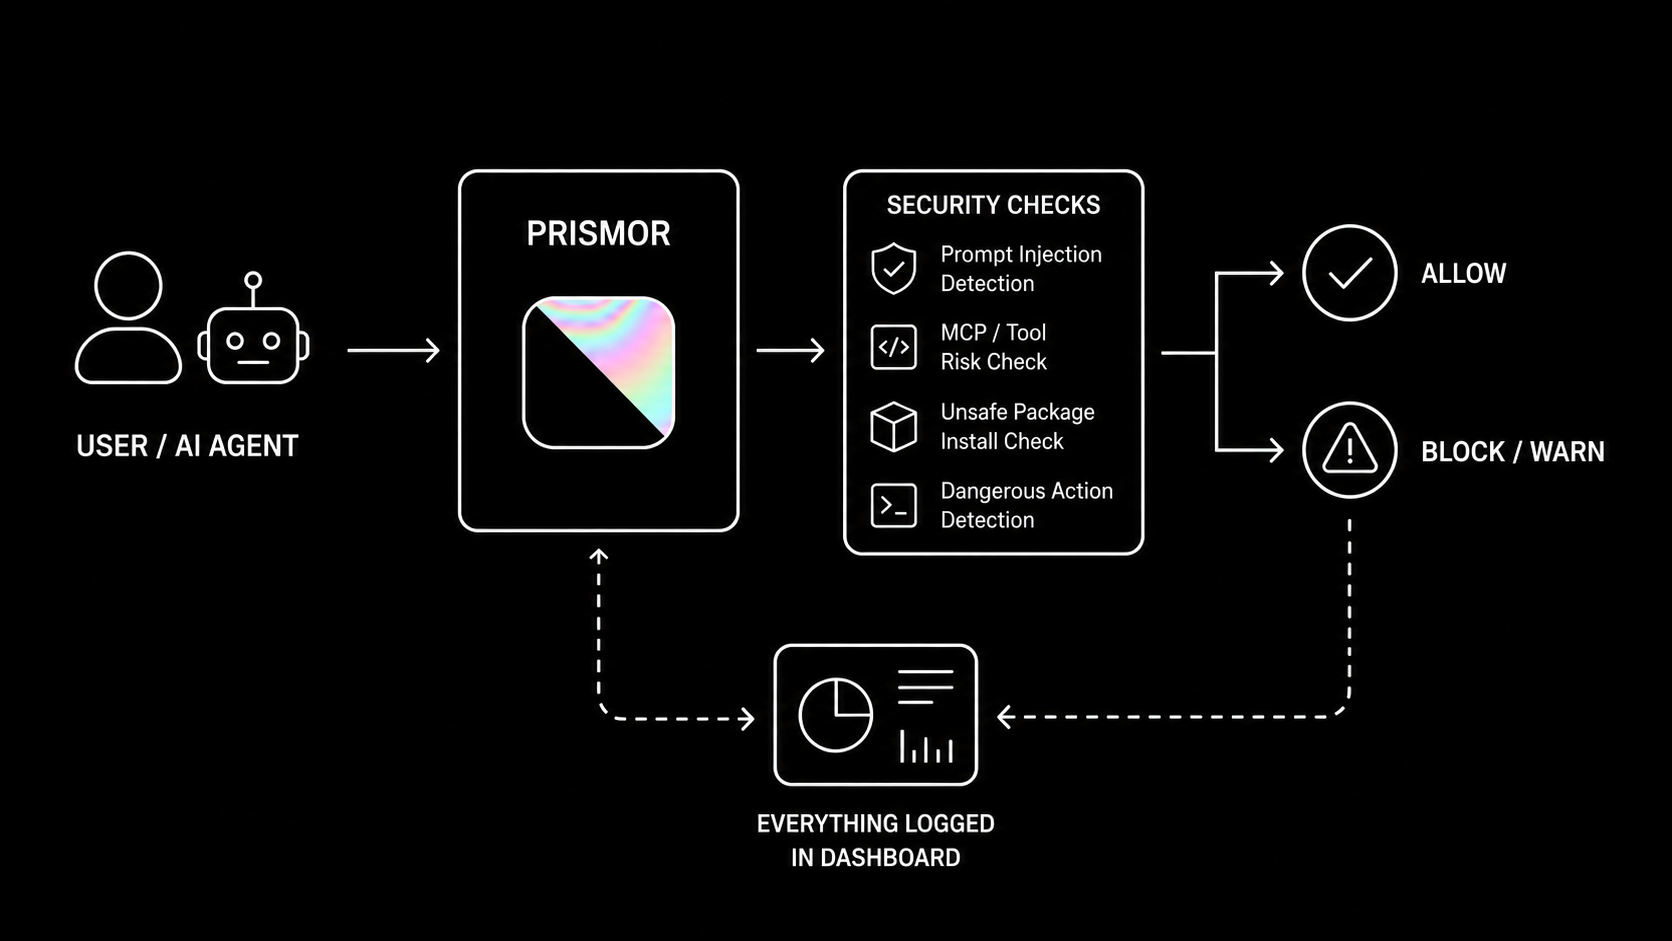
Prismor is an open-source runtime security layer for AI agents that intercepts tool calls, applies policy before execution, masks secrets, and records an audit trail. Its core argument is pragmatic: production agent security requires defense in depth because no single detection technique covers every failure mode.
// ANALYSIS
The right answer to agent security is less a magic detector than a well-placed execution boundary. Prismor’s strongest idea is policy at the tool-call layer, though its value depends on complete hook coverage and maintainable policies.
- –Pre-execution interception can block destructive commands and secret exfiltration even when model judgment fails
- –Observe-versus-enforce modes let teams measure false positives before blocking workflows
- –MCP and framework adapters help close gaps beyond standalone coding-agent CLIs
- –Local, self-hosted audit trails and policy-as-code fit developer and security-team workflows
- –Semantic detection still has blind spots, so least privilege, egress controls, secret cloaking, and human approval remain necessary
// TAGS
prismoragentsecurityguardrailstool-usemcpopen-sourceinfrastructure
DISCOVERED
46d ago
2026-08-24
PUBLISHED
46d ago
2026-08-24
RELEVANCE
8/ 10
AUTHOR
prismor_dev