OPEN LINK ↗
// 3h agoOPENSOURCE RELEASE
AiSOC v21.0.0 Tightens Correlation, Model Provenance
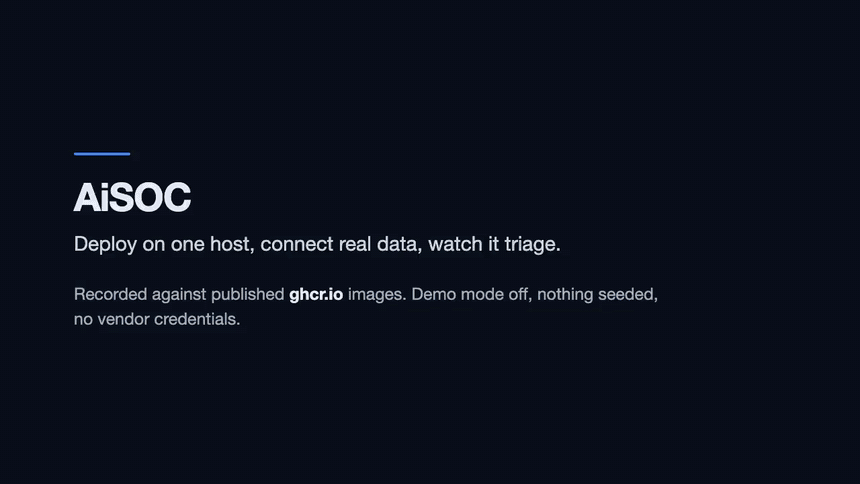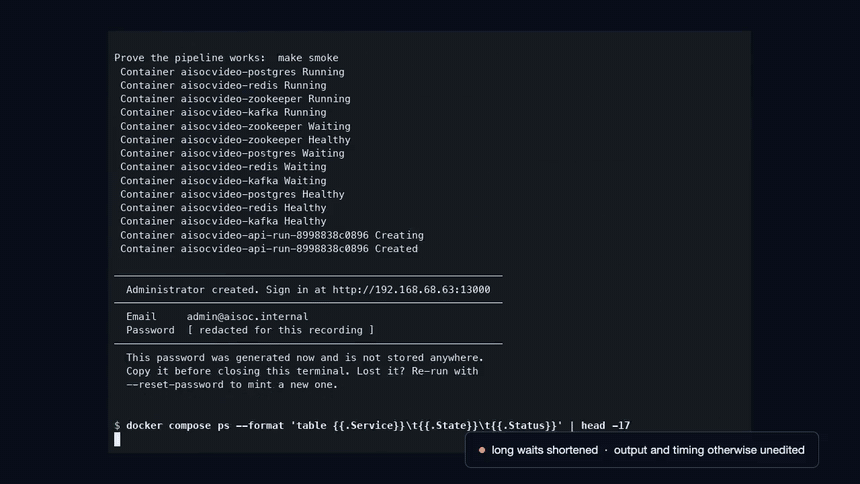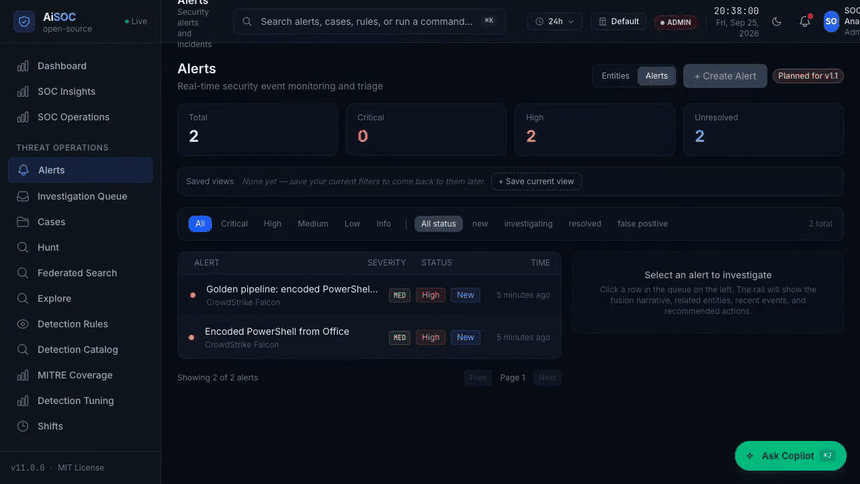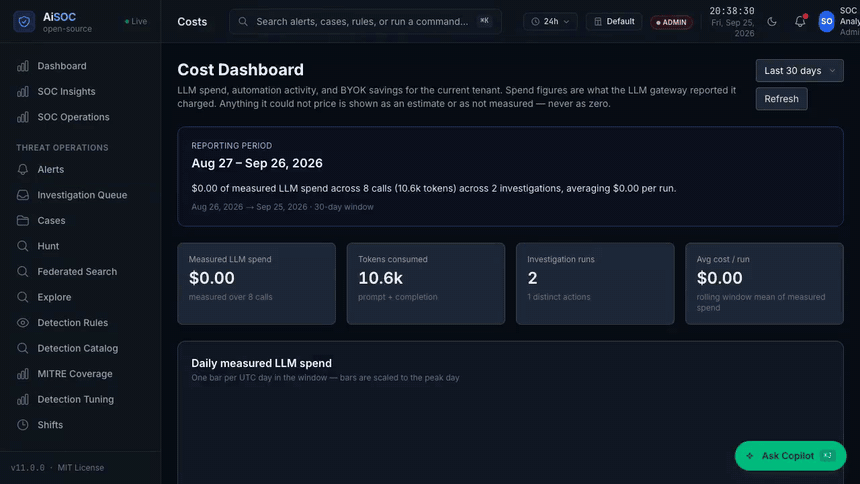
AiSOC v21.0.0 narrows alert correlation when identifiers are missing and adds end-to-end serving-model attribution for verdict evaluations. The release also brings asset criticality into triage, queue priority, and response approval while adding agent-activity ingestion and escalation workflows. [Release notes](https://github.com/beenuar/AiSOC/releases/tag/v21.0.0)
// ANALYSIS
This is a trust-and-correctness release for AI-assisted security operations, prioritizing explainable grouping and evidence over inflated detection metrics.
- –Missing identifiers no longer cause unrelated alerts to merge across rules, reducing measured grouping from 42.6% to 24.5% on the tested cohort.
- –Scorecards now distinguish verified, self-reported, unattributed, and mismatched serving models, making evaluation results more auditable.
- –Asset criticality affects confidence, investigation order, and approval impact without escalating read-only or irreversible actions.
- –The new Agentmetry template maps coding-agent activity into ATT&CK/ATLAS-aware detections while preserving severity and technique metadata.
- –The breaking correlation change means existing incidents remain untouched, but future deployments should revisit alert-volume and incident-rate baselines.
// TAGS
aisocsecurityagentmcpopen-sourceself-hostedevaluation
DISCOVERED
3h ago
2026-11-01
PUBLISHED
10h ago
2026-11-01
RELEVANCE
9/ 10